Web security
Posts with this tag
Posts
-
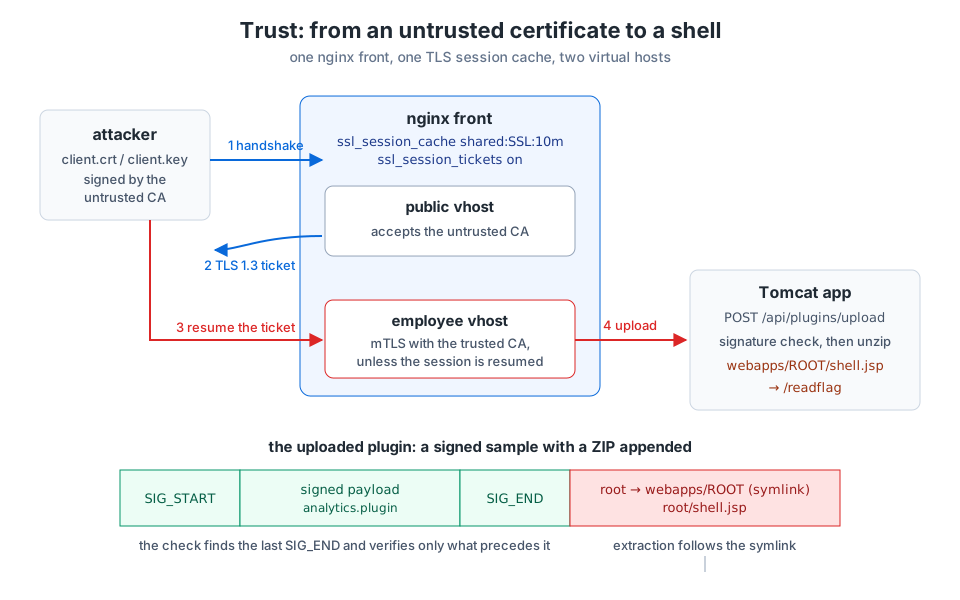
Trust Across Virtual Hosts: Resuming a TLS 1.3 Session Past mTLS, Then a Signed Plugin to RCE
A write-up of the web challenge Trust from WannaGame Championship 2025, where a TLS session cache shared between two nginx virtual hosts lets a ticket from the public site skip client-certificate checks on the employee site, and a plugin upload that verifies a signature but extracts appended data and symlinks plants a JSP shell.
-
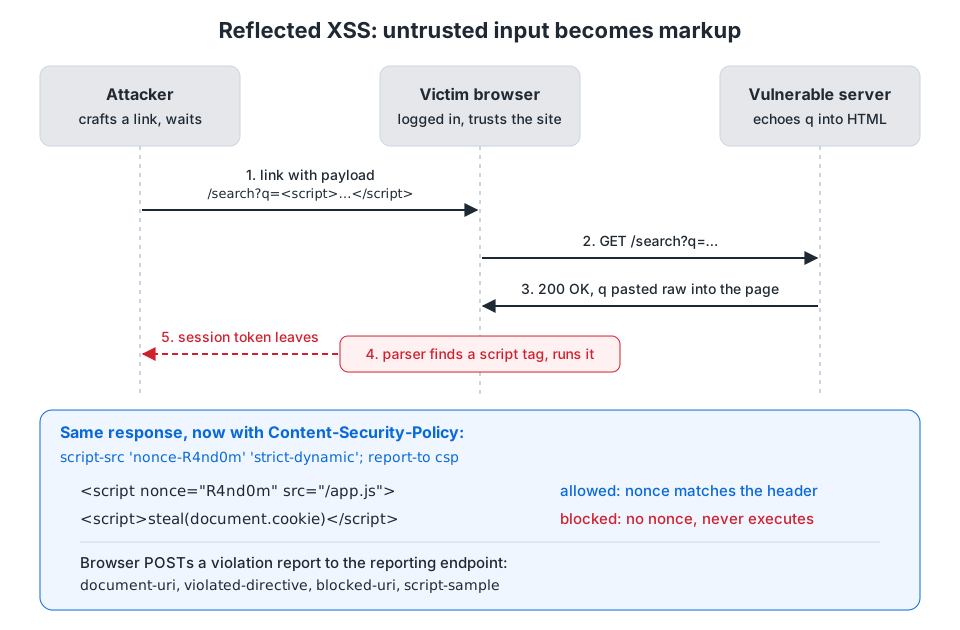
From Reflected XSS to a Real Content-Security-Policy
How script injection actually happens, why output encoding and CSP are different layers, and how to roll out a nonce-based policy without breaking production.