seccomp
Posts with this tag
Posts
-
just-exit: Getting a Shell by Asking for a Syscall That Is Forbidden
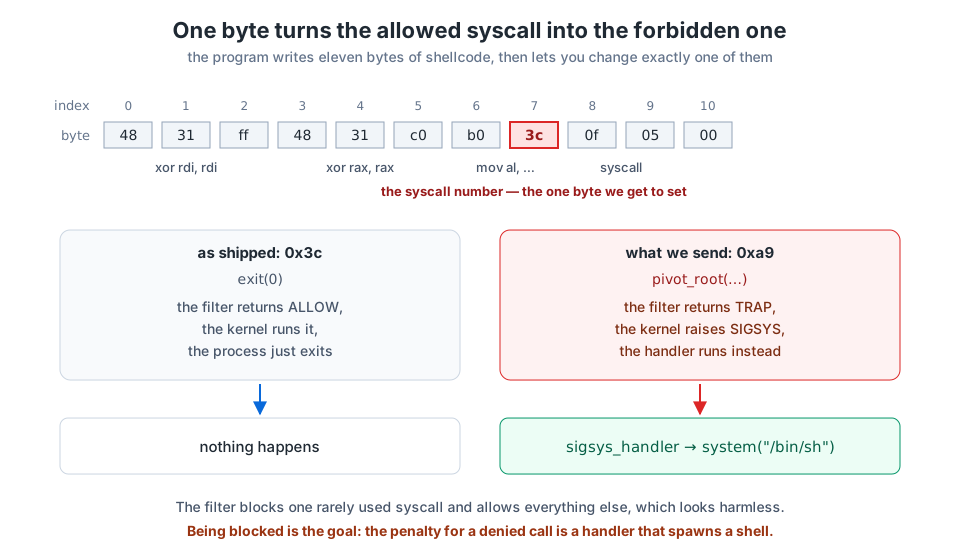
A write-up of the pwnable challenge just-exit from DreamHack CTF Season 7, where every modern mitigation is on and the exploit is a single byte, because the seccomp filter answers a denied syscall with SIGSYS and the program's SIGSYS handler calls system.