Cryptography
Posts with this tag
Posts
-
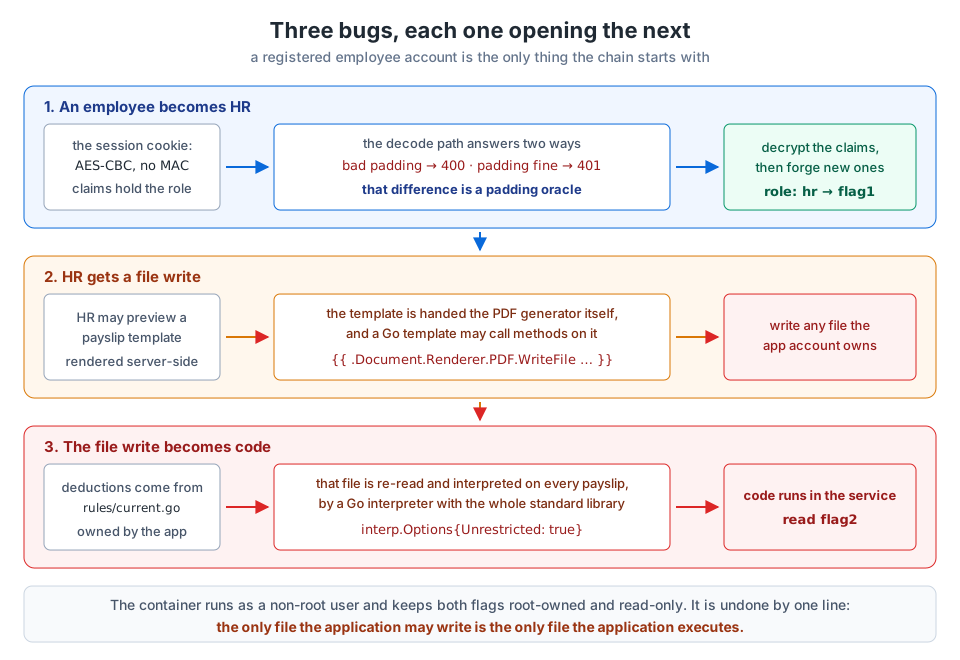
The CSC 2026 Payslip Portal: Three Bugs Where the File You Can Write Is the File You Run
Part two of the CSC 2026 finals. After the ransomware recovery came the attack-and-defence round, and one service fell to a chain of three — an unauthenticated CBC cookie became a padding oracle that forged an HR role, an HR-only template preview handed the live PDF generator to a Go template and turned it into a file write, and that file write landed on the one Go source the service re-interprets on every payslip.
-
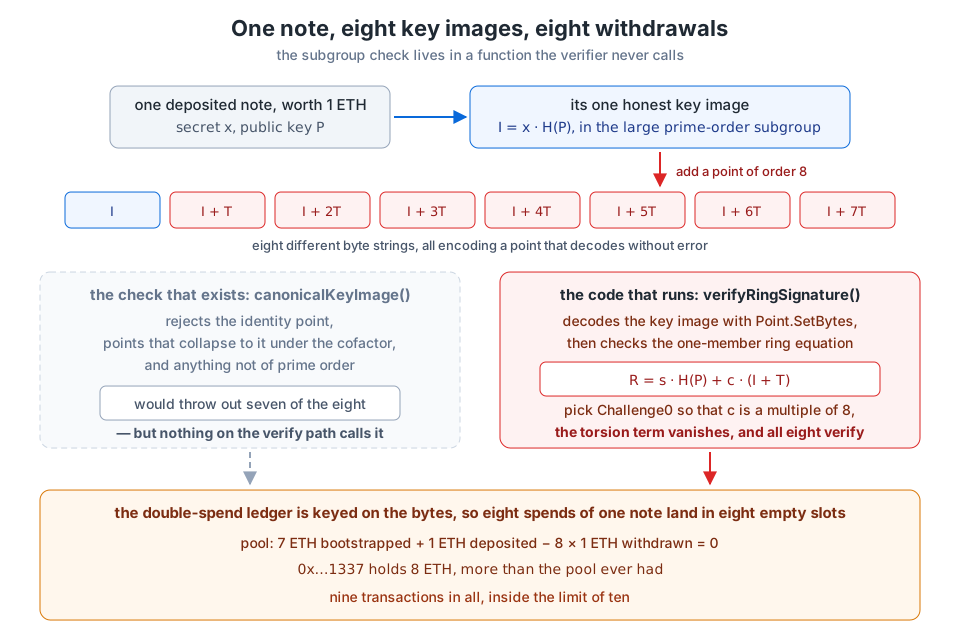
conero: Spending One Note Eight Times Because the Subgroup Check Is in the Wrong Function
A write-up of the blockchain challenge conero from the Codegate 2026 qualifiers, where a patched geth implements Monero-style ring signatures, writes a careful canonical-key-image check, and then verifies proofs in a function that never calls it — so one note yields eight key images and drains the pool.
-
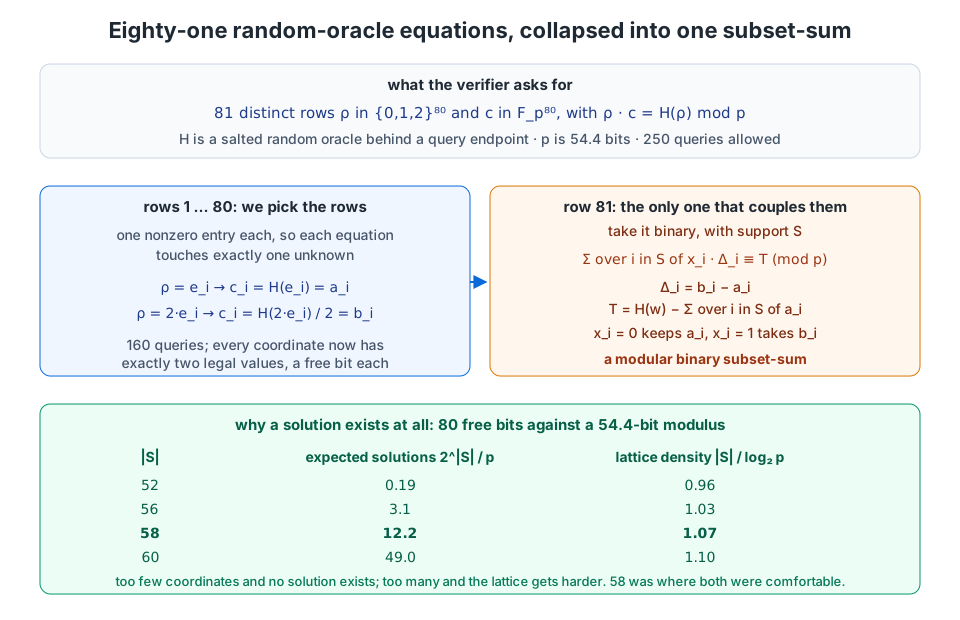
Small ROS: Eighty-One Random-Oracle Equations That Collapse Into One Subset-Sum
A write-up of the crypto challenge Small ROS from the m0leCon 2026 finals, where choosing the rows of an overdetermined random-oracle system turns eighty of its equations into coordinate lookups, leaves one, and reduces the whole verifier to a modular subset-sum that a lattice solves.
-
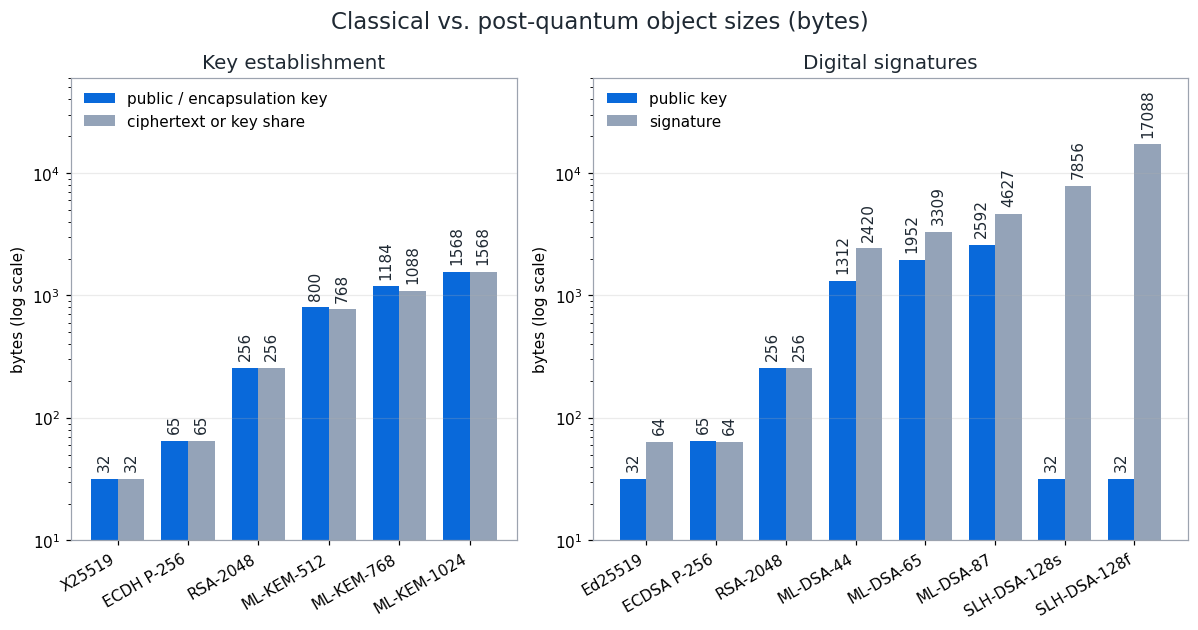
A Post-Quantum Cryptography Primer: Shor, Grover, ML-KEM and the Hybrid Handshake
Which parts of today's cryptography a large quantum computer would break, what NIST standardised in FIPS 203, 204 and 205, how X25519MLKEM768 protects TLS 1.3 sessions, and how to try ML-KEM yourself with OpenSSL 3.5.
-
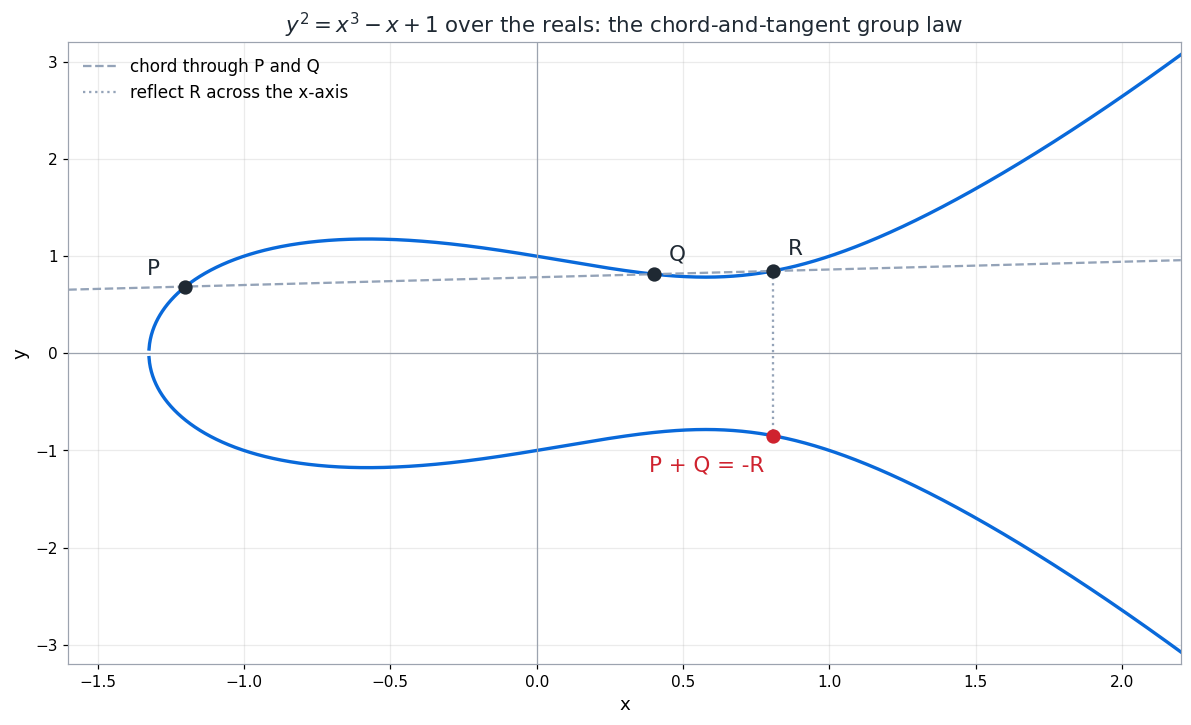
Elliptic Curves from Scratch: Group Law, Double-and-Add and a Toy ECDH
Building elliptic-curve cryptography up from the chord-and-tangent rule to scalar multiplication and a working Diffie–Hellman exchange on a 103-point curve, then showing exactly why that curve is worthless.
-
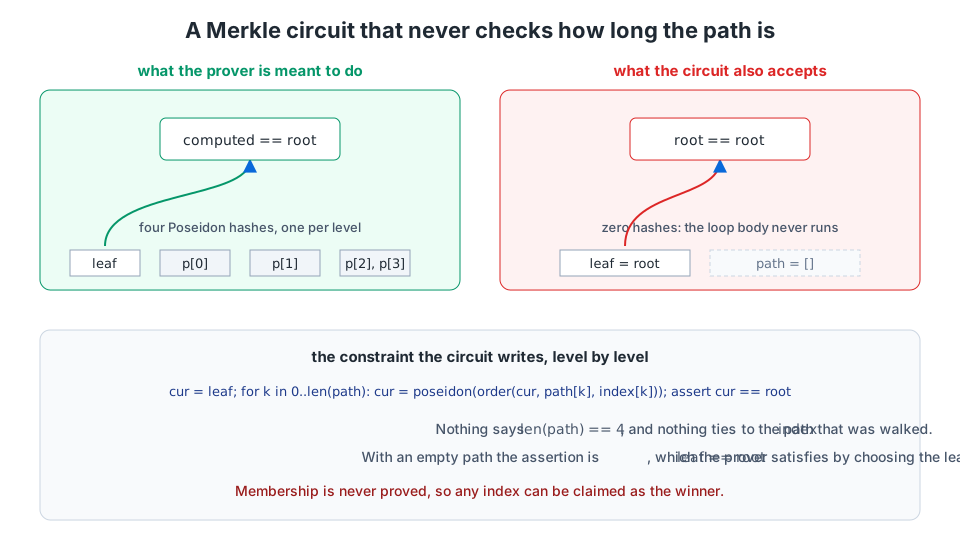
King Halo: When a Zero-Knowledge Circuit Forgets to Constrain the Path Length
A write-up of the crypto challenge King Halo from WannaGame Championship 2025, where a Halo2 Merkle circuit verifies a path without constraining its length, so an empty path reduces the whole proof to leaf equals root and membership is never proved at all.
-
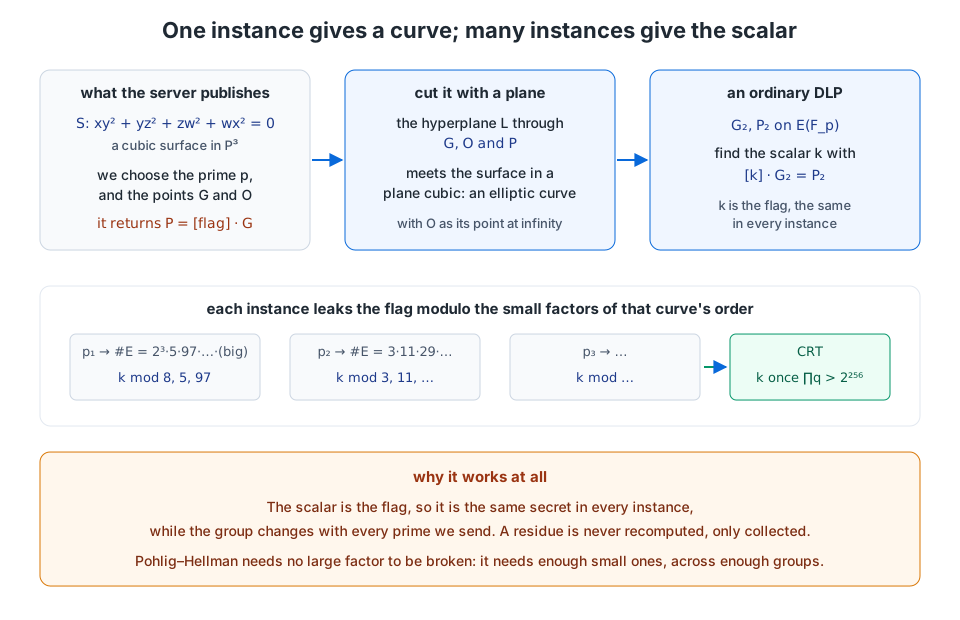
CO: A Cubic Surface, a Hyperplane Section, and a Flag Collected One Small Prime at a Time
A write-up of the crypto challenge CO from WannaGame Championship 2025, where the group lives on a cubic surface in projective 3-space, a hyperplane through the given points cuts it into an ordinary elliptic curve, and the same secret scalar reused across attacker-chosen primes falls to Pohlig-Hellman and the CRT.
-
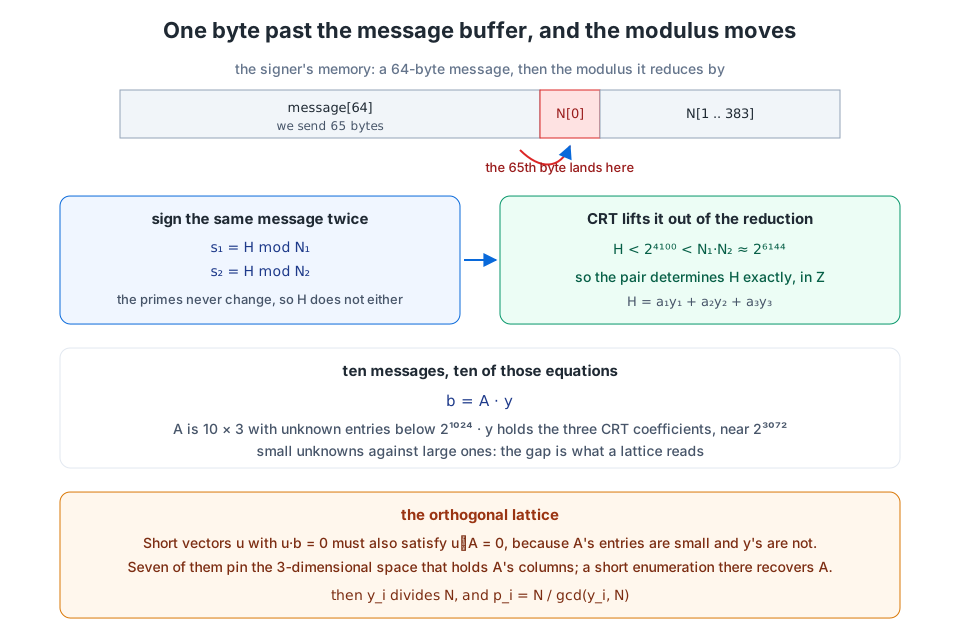
Interesting Signing: One Byte Into the Modulus, Then an Orthogonal Lattice Factors It
A write-up of the crypto challenge Interesting Signing from WannaGame Championship 2025, where a one-byte overflow into the RSA modulus turns the CRT recombination into a linear equation over the integers, and ten of those equations let an orthogonal lattice recover the private CRT coefficients and factor a 3072-bit modulus.